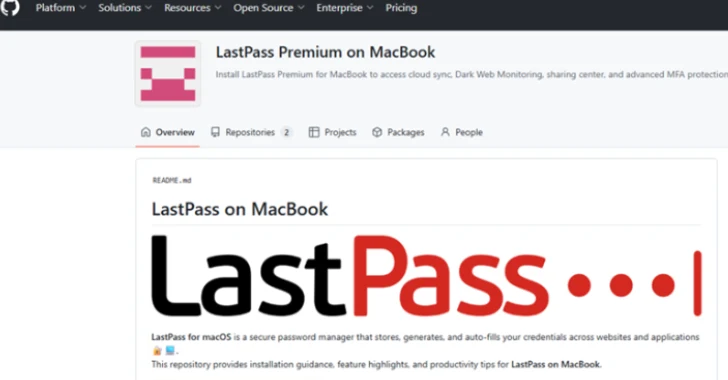
LastPass is warning of an ongoing, widespread information stealer campaign targeting Apple macOS users through fake GitHub repositories that distribute malware-laced programs masquerading as legitimate tools.
“In the case of LastPass, the fraudulent repositories redirected potential victims to a repository that downloads the Atomic infostealer malware,” researchers Alex Cox, Mike Kosak, and Stephanie Schneider from the LastPass Threat Intelligence, Mitigation, and Escalation (TIME) team said.
Beyond LastPass, some of the popular tools impersonated in the campaign include 1Password, Basecamp, Dropbox, Gemini, Hootsuite, Notion, Obsidian, Robinhood, Salesloft, SentinelOne, Shopify, Thunderbird, and TweetDeck, among others. All the GiHub repositories are designed to target macOS systems.
The attacks involve the use of Search Engine Optimization (SEO) poisoning to push links to malicious GitHub sites on top of search results on Bing and Google, that then instruct users to the download the program by clicking the “Install LastPass on MacBook” button, redirecting them a GitHub page domain.
“The GitHub pages appear to be created by multiple GitHub usernames to get around takedowns,” LastPass said.
The GitHub page is designed to take the user to another domain that provides ClickFix-style instructions to copy and execute a command on the Terminal app, resulting in the deployment of the Atomic Stealer malware.
It’s worth noting similar campaigns have been previously leveraged malicious sponsored Google Ads for Homebrew to distribute a multi-stage dropper through a bogus GitHub repository that can run detect virtual machines or analysis environments, and decode and execute system commands to establish connection with a remote server, per security researcher Dhiraj Mishra.
In recent weeks, threat actors have been spotted leveraging public GitHub repositories to host malicious payloads and distribute them via Amadey, as well as employ dangling commits corresponding to an official GitHub repository to redirect unwitting users to malicious programs.